20 April, 2025
Beyond the Password: Why Multi-Factor Authentication is
an Essential Security Upgrade.
Most of us rely on passwords to protect everything from email
and bank accounts to social media profiles. But here's the truth:
passwords just aren't enough anymore. Even if your password is long,
complicated, and totally unique, it can still be stolen, guessed, or
leaked in a data breach. Think of it as locking your front door but
leaving the window wide open; anyone determined enough can still get in.
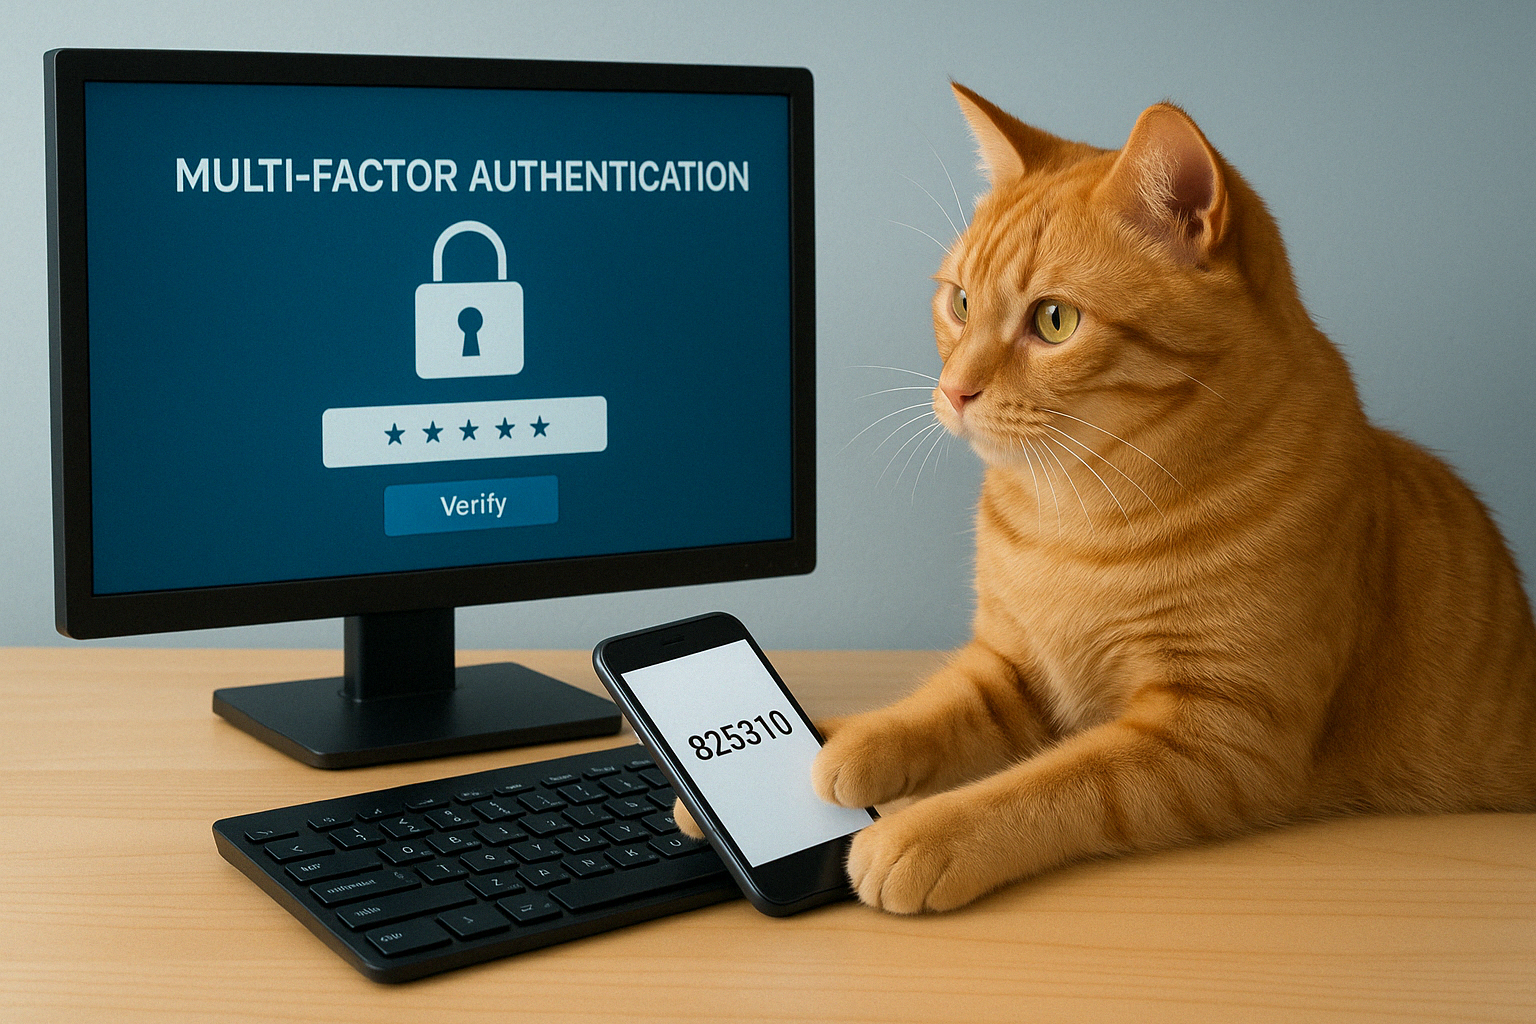
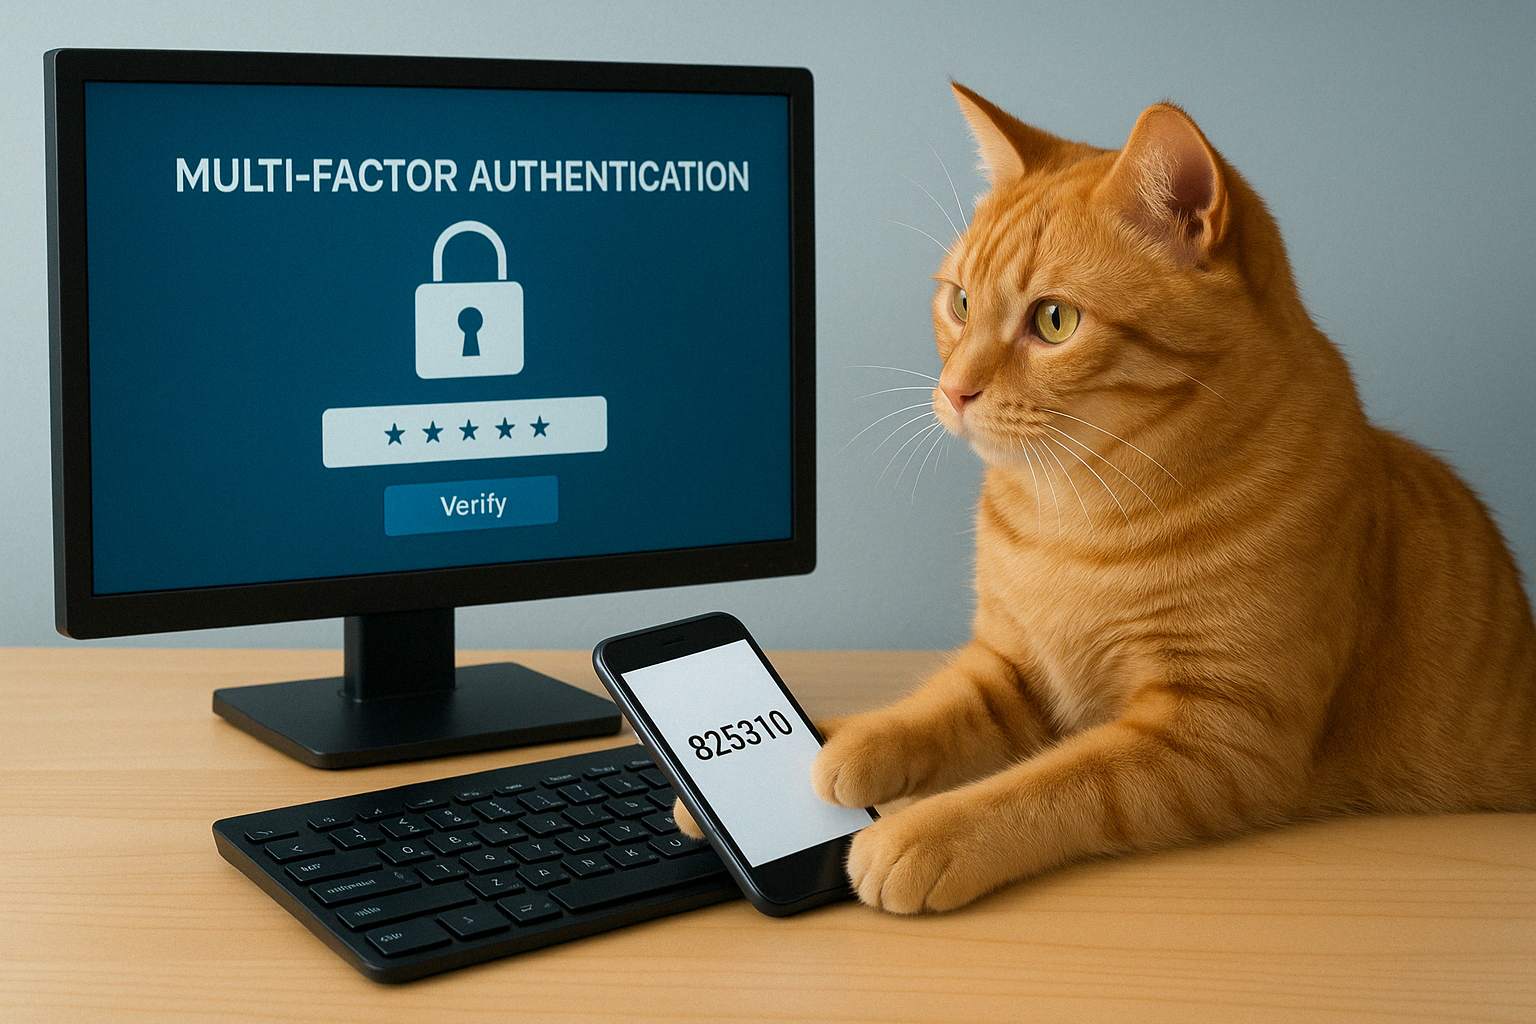
That's where Multi-Factor Authentication (MFA) comes in. Also called
Two-Factor Authentication (2FA) or two-step verification, MFA is like
adding an extra layer of armor to your online accounts. It's become such a
big deal that companies like Google, Apple, and major banks strongly recommend
or even require it. Using MFA makes you way less likely to fall victim to online
scams, identity theft, or account takeovers.
What Is MFA, and Why Does It Matter?.
Multi-Factor Authentication is all about using more than one way to prove it's really
you logging in. Instead of just entering a password, MFA asks for one or two more pieces
of evidence, called "factors." The idea is that even if one piece (like your password)
gets compromised, hackers still can't access your account without the other.
These factors usually fall into three categories:
1. Something You Know – Like your password, a PIN, or the answer to a security question.
2. Something You Have – A physical object you own, such as your phone, a security key, or a smart card.
3. Something You Are – Your fingerprint, face scan, or voice—anything biometric.
Real MFA requires at least two different types of factors. Just having two passwords doesn't
count because they're both things you know. It's the mix of different types that makes MFA
effective.
Think of using an ATM: You need your debit card (something you have) and your PIN
(something you know). Even if someone steals your card, they still need your PIN to take
your money. MFA applies that same logic to protect your digital life.
Why Passwords Alone Aren't Safe.
Hackers are really good at getting around passwords. Here are a few ways they do it:
• Phishing – They trick you into entering your password on a fake website.
• Credential Stuffing – If your password was leaked in one breach, they'll try it on
other accounts.
• Brute Force Attacks – They use software to quickly guess thousands of passwords.
• Password Reuse – If you reuse the same password on multiple sites, one stolen password
gives access to many accounts.
MFA makes all of this much harder. Even if a hacker steals your password, they'd still need your
second factor—like your phone or fingerprint—to get in. Studies from Microsoft and Google show that
enabling MFA can block over 99% of account hacking attempts. That's not just a little better,
it's a vast improvement.
Choosing the Right MFA Method.
When you set up MFA, you'll get a few options for that second step. Some are stronger than others:
Authenticator Apps (TOTP)
• Apps like Google Authenticator or Authy create temporary 6-digit codes you enter when logging in.
These codes change every 30 seconds and are generated by your phone, not sent over the internet.
• Pros: More secure than text messages, works even offline.
• Cons: You'll need to set up backup options in case you lose your phone.
Hardware Security Keys (FIDO Keys)
• Physical devices like a YubiKey or Google Titan Security Key plug into your computer or connect via
NFC. They prove your identity without you needing to enter a code.
• Pros: The most secure options are phishing-proof.
• Cons: It costs money, and you have to carry them around.
SMS or Voice Codes
• Codes are sent via text or phone call. These are still common, but they're also the least secure.
Hackers can steal your phone number using a trick called SIM swapping or intercept the messages in other
ways.
• Pros: Easy to use, but…
• Cons: Not recommended by security experts anymore.
• Biometrics
• Things like fingerprints or face scans are often used to unlock a device, where you store your
second factor rather than as a factor on its own.
• Pros: Super convenient.
• Cons: Not always treated as a full MFA method.
The bottom line is that any MFA is better than none. But if you want the best protection, use a
phishing-resistant method like a hardware security key or an authenticator app.
But Isn't MFA a Hassle?.
Some people avoid MFA because they think it's annoying or too complicated. But the reality is
that it's usually just a small extra step and often only required when you sign in on a new
device or from a new location.
• Quick and Easy: Most MFA steps take just a few seconds. You tap a push notification,
enter a code, or plug in a key.
• Less Stress: Knowing your accounts are much safer gives you peace of mind.
• Fewer Password Issues: With strong MFA, you might not need ultra-complicated passwords
anymore, and you won't have to reset them as often.
• Backup Plans Exist: Are you worried about losing your phone or key? Services let you
set up backup codes or recovery options. Just make sure you store those backup codes safely, ideally
offline.
Companies are also making MFA more user-friendly, and many are moving toward systems that adapt based on
risk, such as only asking for the second factor if something seems suspicious.
Final Thoughts: Turn It On.
Passwords aren't going away anytime soon, but they shouldn't be your only defense. In today's world,
Multi-Factor Authentication is essential. It drastically reduces your chances of getting hacked and
is one of the easiest things you can do to protect yourself online.
So don't wait. Go into the security settings of your email, bank, and social media accounts and turn
MFA on, especially for your most important accounts. It only takes a few minutes and could save you
from a major headache later.
Protect your digital life. Lock it down with MFA.